A service account is a domain account used to run an application, Windows service, or scheduled task. Most service accounts are regular user accounts, so there is no single attribute or flag that identifies them all.
In this guide, I'll show you how to identify service accounts in Active Directory by checking various attributes using PowerShell and the AD Pro Toolkit.
Steps to Find Service Accounts in Active Directory
No single attribute marks an account as a service account, so you work through several signals and build a list. Each step below narrows it down.
1. Look for service account naming patterns
Admins often name service accounts with a specific prefix, below are common service account naming patterns:
svc_*service_*sql_*app_*backup_*
Get-ADUser -Filter {SamAccountName -like "svc_*" -or SamAccountName -like "service_*"} -Properties Description |
Select-Object SamAccountName, Name, Description
This is only a starting point, because naming conventions are not always followed.
2. Check the account description
Check the description on all accounts for these specific words:
Service AccountSQL ServiceApplication AccountBackup ServiceUsed by XYZ application
Get-ADUser -Filter {Description -like "*service*"} -Properties Description |
Select-Object SamAccountName, Name, Description
You can also review the Description field in Active Directory Users and Computers.
3. Find accounts with a Service Principal Name
This is the strongest signal Active Directory gives you. An SPN is registered when an account runs a service that clients authenticate to with Kerberos, so an ordinary user account with an SPN is almost always a service account.
Get-ADUser -Filter {ServicePrincipalName -like "*"} -Properties ServicePrincipalName |
Select-Object SamAccountName, Name, ServicePrincipalName
4. Find accounts where the password never expires
Service accounts are often configured with the password never expires setting, which is a strong signal that an account may be a service account.
Get-ADUser -Filter {PasswordNeverExpires -eq $true -and Enabled -eq $true} -Properties PasswordNeverExpires |
Select-Object SamAccountName, Name
5. Check accounts trusted for delegation
Delegation is granted so a service can act on behalf of a user. It is uncommon on a normal account and worth reviewing on security grounds as well.
Get-ADUser -Filter {TrustedForDelegation -eq $true} -Properties TrustedForDelegation |
Select-Object SamAccountName, Name
6. Look for managed service accounts
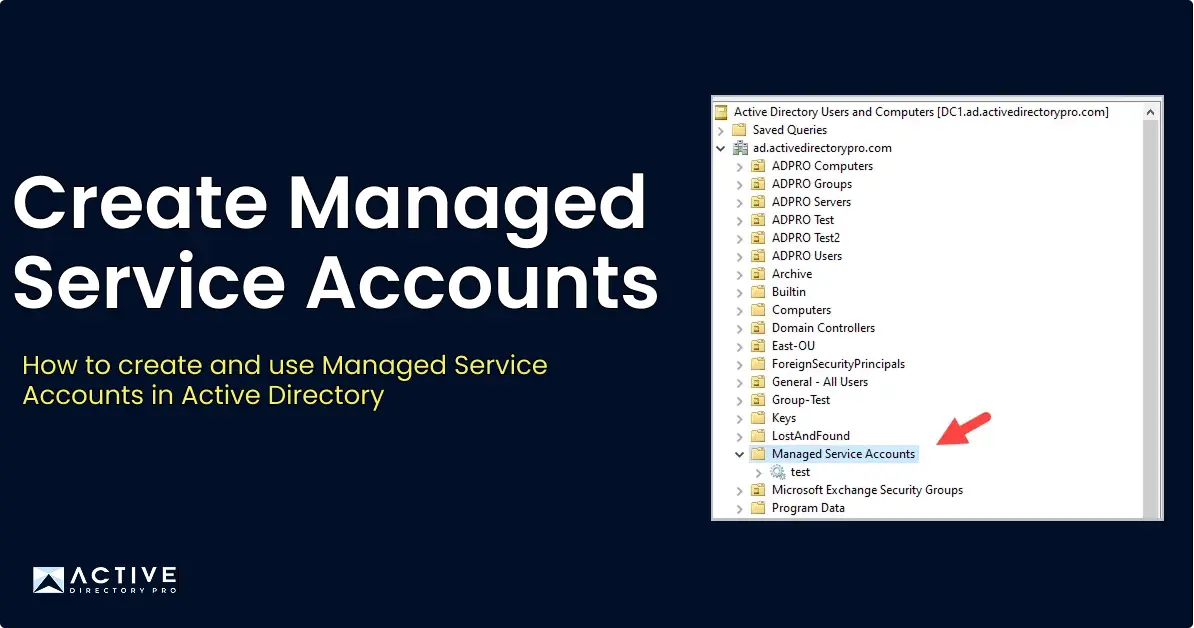
Group managed and standalone managed service accounts are a different object class, so none of the commands above return them.
Get-ADServiceAccount -Filter * | Select-Object Name, HostComputers, Enabled
7. Monitor event logs
Everything above tells you an account looks like a service account. The event logs tell you which accounts are actually being used as one, because Windows records a different logon type for a service than for a person signing in.
- Logon type 5 is a service starting under an account
- Logon type 4 is a scheduled task
- Both appear in event 4624 in the Security log
Get-WinEvent -FilterHashtable @{LogName='Security'; ID=4624} -MaxEvents 500 |
Where-Object { $_.Message -match 'Logon Type:\s+5' }
Logon events are recorded on the computer where the logon happens, so you’re querying one machine at a time, logs can roll over, and you only see what auditing was configured to record. AD Audit Pro collects logon events from every machine in one place and keeps the history, so you can see which accounts are being used to run services across the domain without checking servers one by one.
Service Accounts Report with AD Pro Toolkit
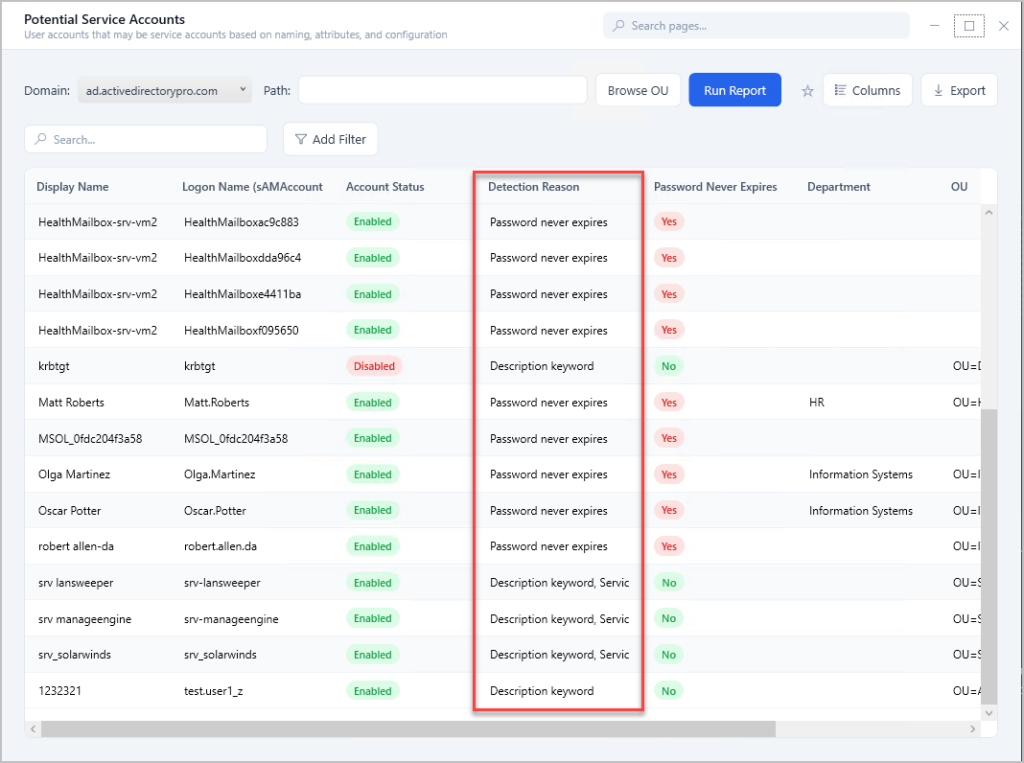
Instead of manually running multiple PowerShell cmdlets, the AD Pro Toolkit combines these checks into a single report. The report reads Active Directory attributes only. It does not check whether an account is actually running a service on a computer.
-
Browse to Reports > Security > Potential Service Accounts
-
Click “Run Report” to check Active Directory for service accounts.
-
Review the list of accounts and the detection reason.
-
To export the report click the export button.
Find Where Service Accounts are being used
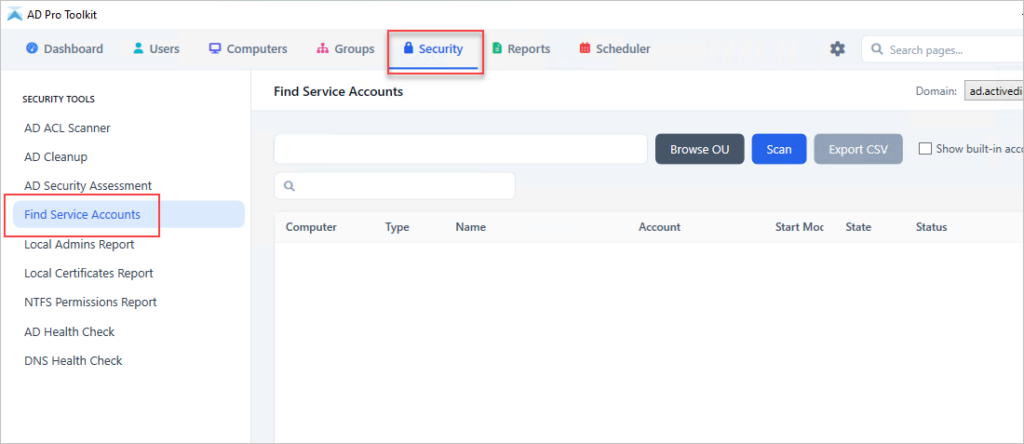
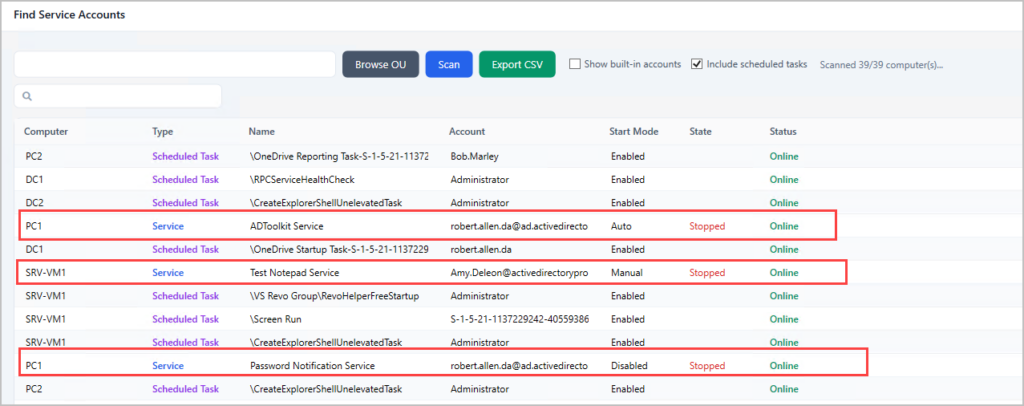
The AD Pro Toolkit also includes a report that scans domain-joined computers to find where service accounts are being used. It checks Windows services and scheduled tasks on each computer and shows which account is running them.
-
Click on Security > Find Service Accounts
-
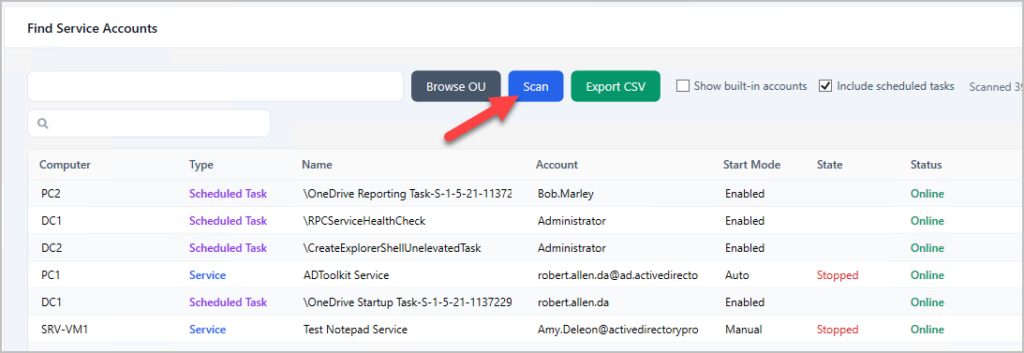
Click “Scan” to check all computers for service accounts. To scan specific computers click “Browse OU” and select an OU.
-
Review the scanned results. They can be filtered, searched and exported to CSV.
In the screenshot below it found multiple Windows services running with domain accounts, showing the computer, type, name and the account running the service.
Try the AD Pro Toolkit free for 14 days
Best Practices for Managing Service Accounts
Service accounts are ordinary domain user accounts, so there is no easy way to list them unless you have made them identifiable in advance. These practices do that.
-
Use a naming prefix. Microsoft recommends prefixing service accounts with something like
svc-so they are easier to find and manage. -
Fill in the description field. Record what the account is for and who owns it, such as a team alias or the security owner. This is what makes searching by description worth doing.
-
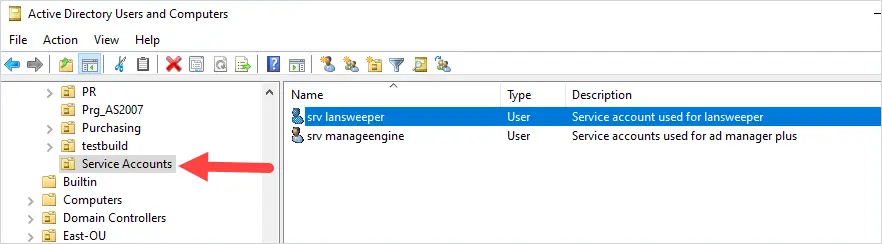
Put them in their own OU. You will have existing accounts you cannot rename, so an OU gives you one place to list them all regardless of what they are called.
-
Check the Log on as a service right. An account configured to run a service is granted this right, which you will find under Computer Configuration > Windows Settings > Security Settings > Local Policies > User Rights Assignment. In the screenshot below two domain accounts have been granted it.
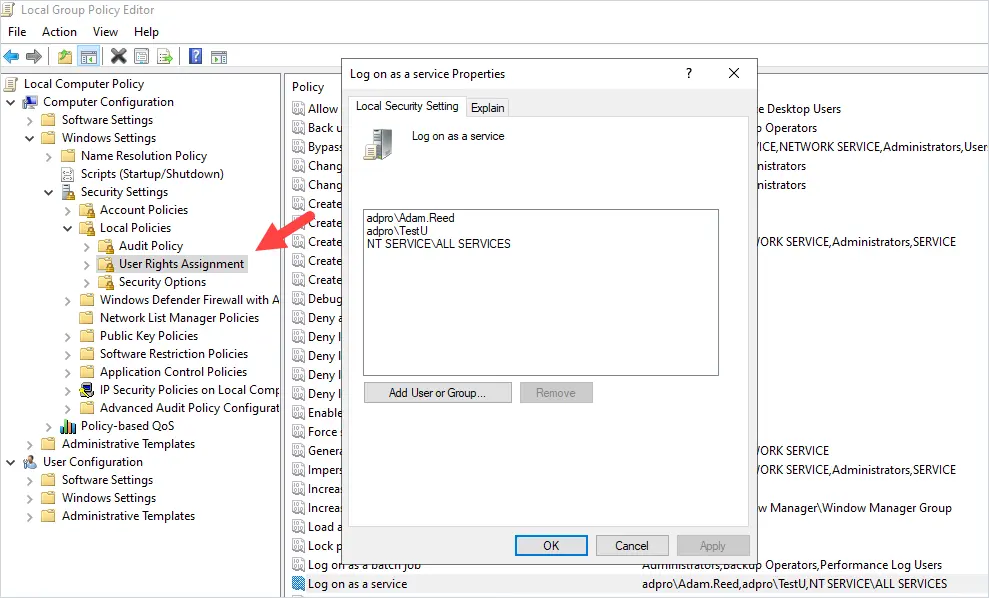
This one is per machine, so there is no simple way to query it across every computer. PowerShell or the service accounts report is the practical way to cover the whole domain.
Resources
- Securing on-premises service accounts - Microsoft documentation on service accounts, types, how to find service accounts and proper documentation.
- Get-WmiObject - Microsoft command documentation. This is the command used to search for windows services.