Active Directory has no built-in "inactive" flag, so there is nothing to simply filter on. Instead, you find inactive accounts by comparing each user's last logon attribute, normally lastLogonTimestamp, against a date you choose. Any enabled account whose last recorded logon is older than that date is treated as inactive. Keep in mind that lastLogonTimestamp only refreshes every 14 days, so pick a threshold of at least 30 days to avoid false positives.
In this guide, I'll show you how to use PowerShell to find inactive users who have not logged on in at least 60 days. You can customize the inactive timeframe.
Method 1: Find Inactive AD Users with PowerShell
To find inactive accounts with PowerShell you will need the RSAT tools installed or run these commands on the domain controller.
All of these examples use the LastLogonDate property which is the converted value of the LastLogonTimestamp.
-
Open PowerShell as administrator.
-
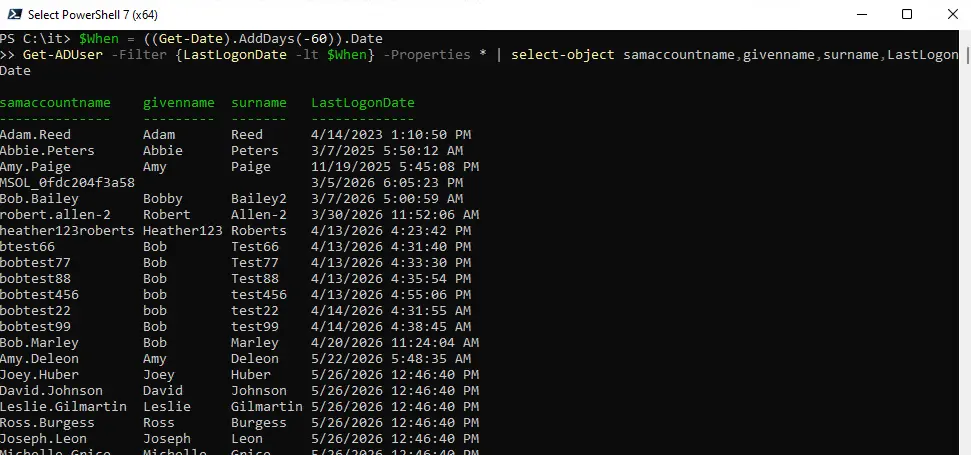
Run the following command, changing the
AddDaysvalue to the period you want to check. In the example below, I'm checking for accounts that have not logged on in at least 60 days.$When = ((Get-Date).AddDays(-60)).Date Get-ADUser -Filter {LastLogonDate -lt $When} -Properties LastLogonDate | Select-Object SamAccountName, GivenName, Surname, LastLogonDateHere is an example from my domain.
-
Export to csv, you can export the results to CSV by adding | export-csv -path c:\ps\inactiveusers.csv
$When = ((Get-Date).AddDays(-30)).Date

Get-ADUser -Filter {LastLogonDate -lt $When} -Properties LastLogonDate |
    Select-Object SamAccountName, GivenName, Surname, LastLogonDate |
    Export-Csv -Path c:\ps\inactiveusers.csv -NoTypeInformation
Method 2: Find Inactive User Accounts with the AD Cleanup Tool
The AD Cleanup Tool makes it very easy to find all inactive users in your network. You can then disable, delete, move and export the list of inactive accounts.
-
Click on Security > AD Cleanup
-
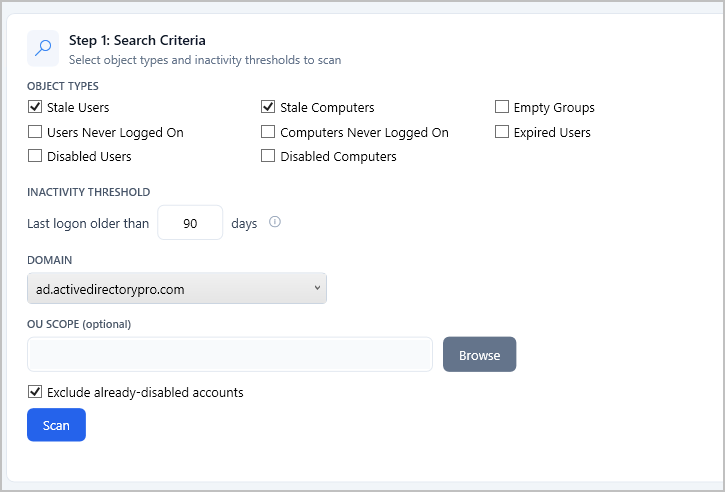
Select object types and the inactivity threshold
-
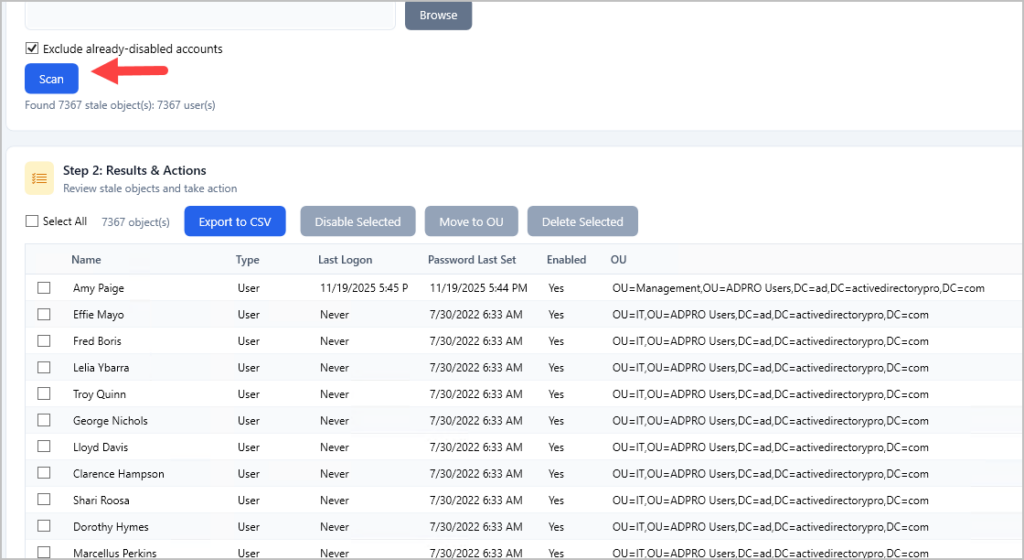
Click “scan” to get a list of inactive accounts.
-
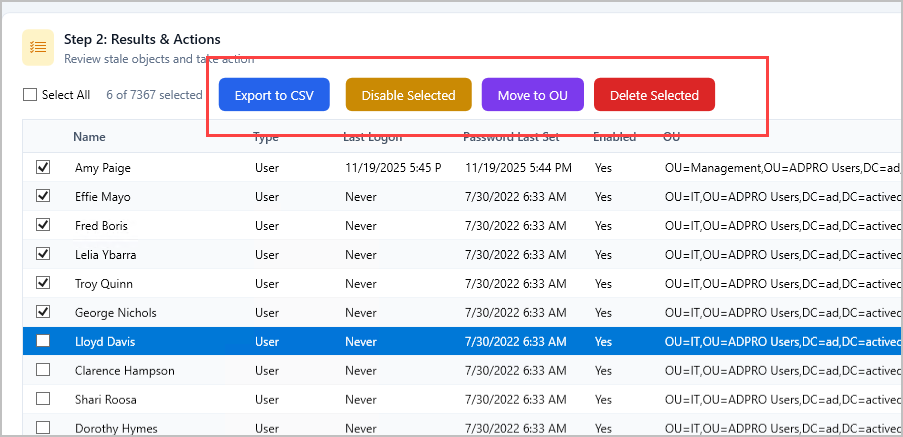
To clean up the stale accounts, select an account and then choose an action.
Method 3: Find Stale User Accounts with ADUC
You can find inactive and stale users by reviewing a user’s lastLogonTimestamp attribute. This attribute is updated when a user logs on to their computer or the network. Typically, you want to find accounts where this attribute has not been updated in a certain period of time such as the last 90 days. This would mean the user has not logged on in 90 days.
To check if an Active Directory user is inactive follow the steps below.
- Click on “Properties” for a user account.
- Click on the “Attribute Editor”.
- View the lastLogonTimestamp value.
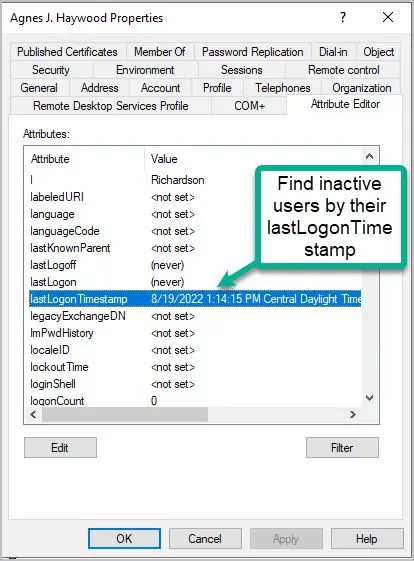
In the screenshot above, you can see the users lastLogonTimestamp has not been updated in a very long time. I would consider this a stale account because it has not been used in over a year.
Find Inactive Users in a Specific OU
The commands above search the whole domain. To limit the search to a single organizational unit, add the -SearchBase parameter with the distinguished name of the OU.
-
Find the distinguished name of the OU.
Get-ADOrganizationalUnit -Filter "Name -eq 'Accounting'" | Select-Object DistinguishedName -
Run the command below, replacing the OU and the
AddDaysvalue with your own.$When = ((Get-Date).AddDays(-60)).Date $OU = "OU=Accounting,OU=ADPRO Users,DC=ad,DC=activedirectorypro,DC=com" Get-ADUser -Filter {LastLogonDate -lt $When} -SearchBase $OU -Properties LastLogonDate | Select-Object SamAccountName, GivenName, Surname, LastLogonDate
-SearchBase searches the whole subtree, so any OUs nested inside Accounting are included. Add -SearchScope OneLevel if you only want the accounts sitting directly in that OU. This is the usual reason a search returns more accounts than expected.
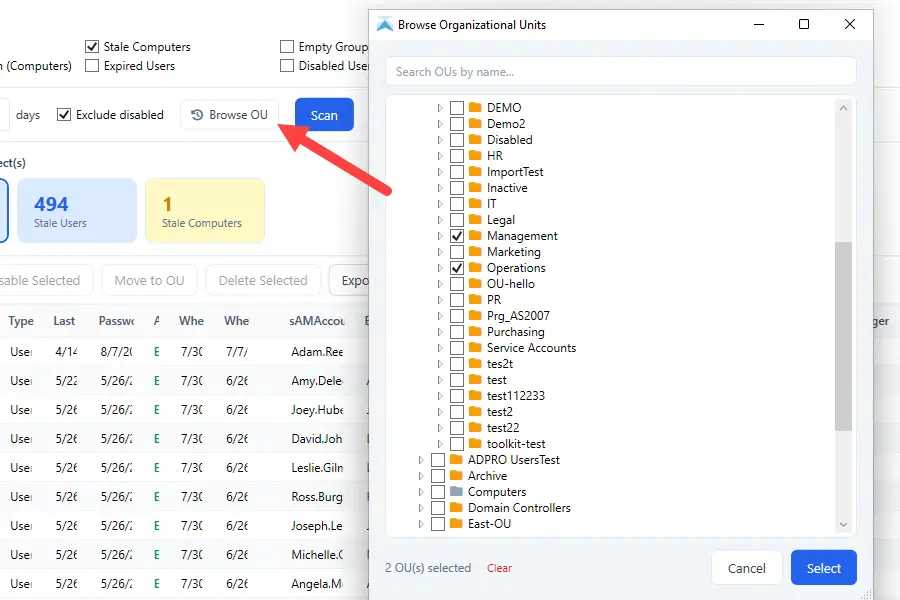
With the AD Cleanup Tool you can click "Browse" and select the OU instead, with no distinguished name to look up.
Best Practices for Inactive User Accounts
Here are some best practices for cleaning up inactive user accounts.
- Use a 45 day threshold. Search for accounts with a lastLogonTimestamp that is 45 days or older, meaning the account shows no logon activity for 45 days or longer.
- Disable before you delete. Never remove an account as soon as it shows up as inactive. Disable it first for at least 30 days, and I typically go with 60. With remote access, VPNs and laptops, AD does not always get updated, and disabling first makes it very easy to re-enable the account and give the user their access back.
- Record why it was disabled. Add a description to the account with the date and your initials. This is very helpful for other admins in case someone asks why an account is disabled.
- Move disabled accounts to a dedicated OU. They are easy to find when the waiting period is up, you can link a restrictive GPO to that one OU, and they stop cluttering the OUs you manage day to day.
- Check hybrid accounts separately. An inactive on-premise account might not mean an inactive Office 365 account. In hybrid environments you could have users working from home who never authenticate against on-prem AD but log into Office 365 daily, which is exactly why disabling first matters more than deleting.
- Run the cleanup every month. A regular cadence keeps the list short and each decision easy.