Monitoring bad password attempts helps you detect brute force attacks, misconfigured services, and accounts with stale credentials. In this guide, I’ll show you how to find bad password attempts for users and computer accounts using PowerShell and the AD Pro Toolkit. I’ll also cover the BadPwdCount and BadPasswordTime attributes and how to automate bad password reports.
How Bad Password Attempts are Recorded in Active Directory
Active Directory tracks bad password attempts using two attributes:
- BadPwdCount - the number of failed logon attempts since the last successful logon. This counter resets to zero after a successful login or when the account lockout observation window expires.
- BadPasswordTime - the timestamp of the last failed logon attempt. This records when the most recent bad password was entered.
These attributes are stored on each domain controller individually and do not replicate between DCs. To get an accurate count, you need to query every domain controller or use the LastBadPasswordAttempt property which is a calculated value that checks all DCs.
Both attributes apply to user accounts and computer accounts. A computer account with a high BadPwdCount may indicate a broken trust relationship or a misconfigured service.
Find Bad Password Attempts using PowerShell
To check bad password attempts for a single user, run:
<code>get-aduser -Identity robert.allen -Properties * | select name, badPwdCount, LastBadPasswordAttempt

In the screenshot above, you can see the account robert.allen has 3 for bad password count and the last bad password attempt was 3/7/2023 at 9:51 AM.
Bad Password Attempts Report using AD Pro Toolkit
The AD Pro Toolkit includes a built-in bad password attempts report that shows all users and computers with failed logon attempts. It displays the BadPwdCount, last bad password time, and account status in one view You can filter by OU, export the results, or schedule the report to run automatically
Browse to Password Reports > User Password Details
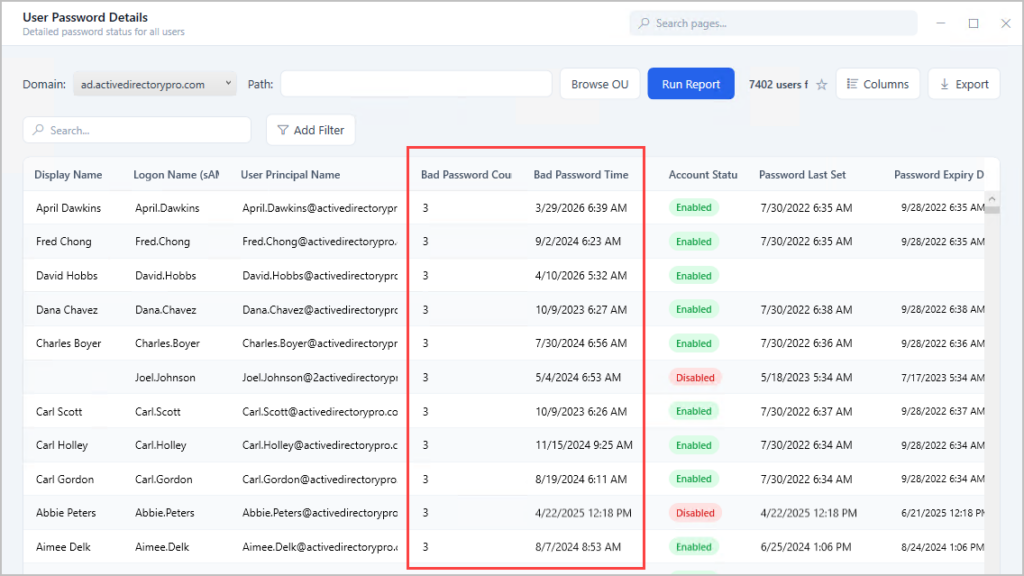
This report can be very useful to audit for suspicious logon attempt activity.
Browse to Computer Reports > All Computers
Click Columns and add the Bad Password Count and Bad Password Time columns.
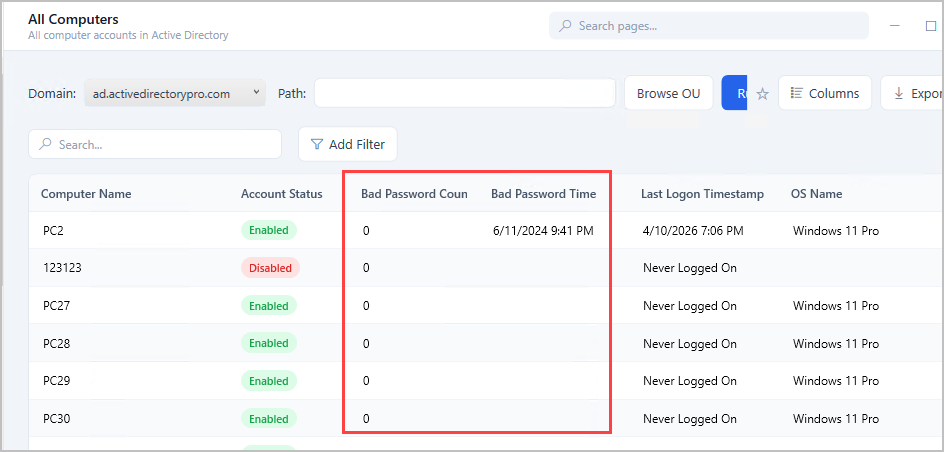
If you see a large number of users with bad password attempts with increasing badPwdCount, this needs to be investigated.
Download Free Trial of AD Pro Toolkit
Find Bad Password Attempts for all users in Active Directory
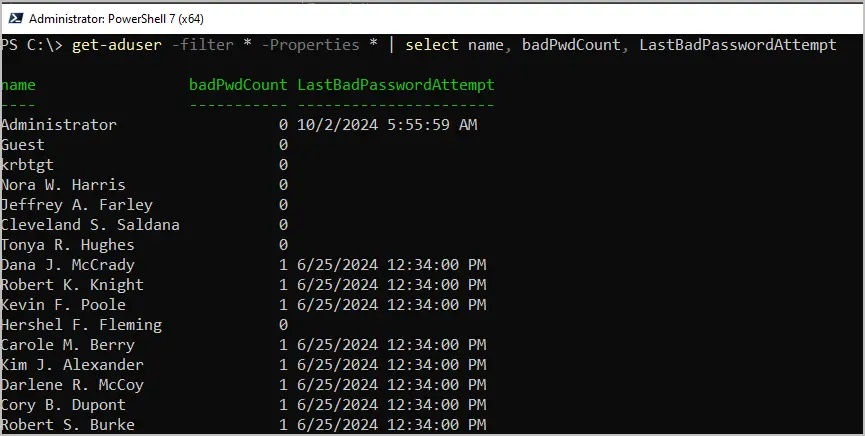
To get all the user’s last bad password attempts use the following command.
get-aduser -filter * -Properties * | select name, badPwdCount, LastBadPasswordAttempt
Automate Bad Password Attempts Report
Manually checking for bad password attempts on a daily basis is inefficient. It is better to automate this report in case you forget and it will also save you time.
To automate this report you can use the task scheduler to get a daily, weekly, or monthly report emailed to you.
Click on Scheduler and then click the Add button.
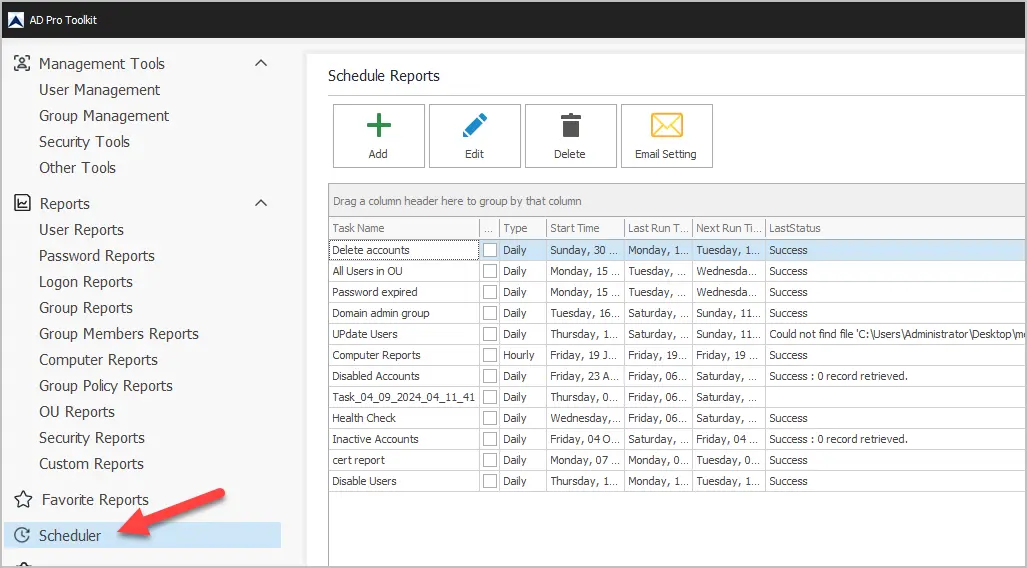
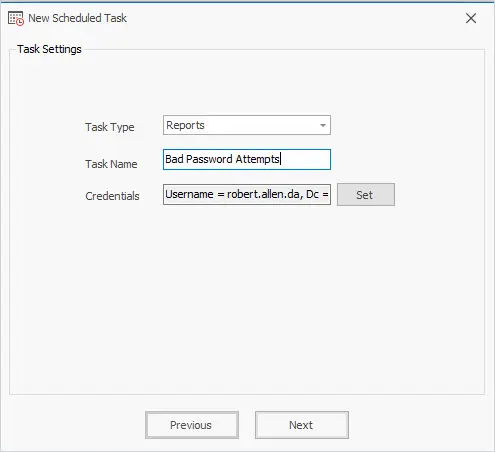
Select Reports
Enter a task name. For example, Bad Password Attempts.
For credentials click on Set and enter your account details.
Click Next.
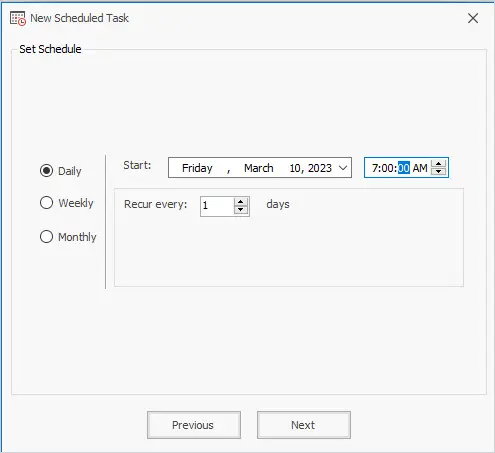
Set the schedule. Choose from Daily, Weekly, or Monthly.
In this example, I’ve set it to run daily at 7:00 AM.
On the last screen for category select User > Password Status
Then select the report you want to automate. In this example, I’ll select “Bad password attempts in last 1 day.
Next, choose the path. You can choose from the entire domain or select an OU or group.
For the output enter an email subject.
Click Finish.
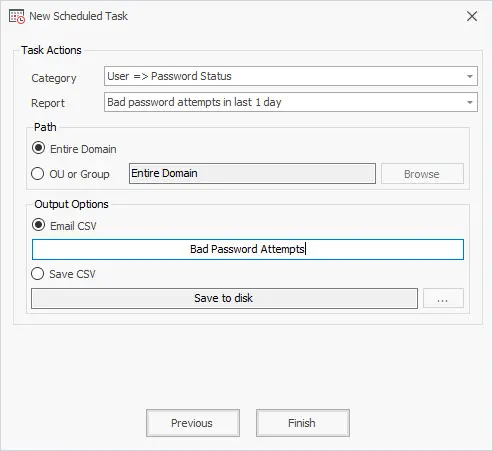
That completes the steps for creating an automated report. You will now get an email according to the schedule you selected that includes a CSV report.
In this article, I showed you two options to check for users with bad password attempts. The bad password time is stored in an Active Directory attribute when a user enters their password incorrectly. You can easily get the bad password time and count by using PowerShell. I also showed you how to automate the bad password report by using the AD Pro Toolkit. The toolkit includes over 200 built-in AD Reports for users, computers, groups, and group policy.